
Posts
2459Following
160Followers
78Also @noisytoot@mice.tel in case chinchillas eat the cables
Noisytoot
noisytoot
RE: https://mastodon.social/@Migueldeicaza/116544740655935047
 1
 0
 1
repeated

Joseph Lorenzo Hall, PhD
joebeone@techpolicy.socialLiving on the East Coast means my radio-controlled atomic wall clock is completely deaf to the atomic (WWVB) signal from Colorado. In the attached video, I am using my smartphone to force the clock to sync to exact Internet time via a clever hardware hack. 1/4
7
4
0

Noisytoot
noisytootNOT ANOTHER ONE
second linux LPE of the day
2
3
1
Noisytoot
noisytootanother linux LPE, this time without even a patch or CVE number yet (but there's a mitigation of preventing esp4, esp6, and rxrpc modules from loading)
0
0
0
repeated
asnev 
asnev@tech.lgbt
if this post gets greater than or equal to four (4) interactions i will make a music in a random* yamaha soundchip
*not really random
1
2
1
 repeated
justsoup 
justsoup@mstdn.social
Being able to unlock the bootloader of a device you own should be legally mandated. I own the hardware, I should own the functionality of it too. I can get the modem being illegal to modify, since that has a ton of regulatory and public safety tape around it, but the OS being irreplacible is dumb.
Also, unlocking the bootloader should be as simple as sending a command to the device. Screw this trend of needing unlock codes (looking at you Motorola, Fairphone, and Co.).
3
4
0
repeated
Merlin
merlin@kif.rocksBoost this if you think DENIC should just hand out free hosts files in the meantime
2
1
0
repeated
Josh "cortex" Millard
joshmillard@mastodon.socialmitosis is just a scam by Big Biology to cell more
27
9
1
repeated

akkoma stuff
akkoma@ihatebeinga.liveupdating! updating!
https://meta.akkoma.dev/t/akkoma-stable-2026-05-akk-host-club/940
0
1
0
repeated
 repeated

dmiException 💽
domi@donotsta.remy dear sysops: where do you store backups? 
i’m looking for something below 2EUR/TB, because otherwise it’s just more cost-effective to buy drives and create a small backup server…
the whole thing would be in the ballpark of 30-40TB, so if you want to suggest hetzner storageboxes… uh…
17
2
0
repeated
Hailey
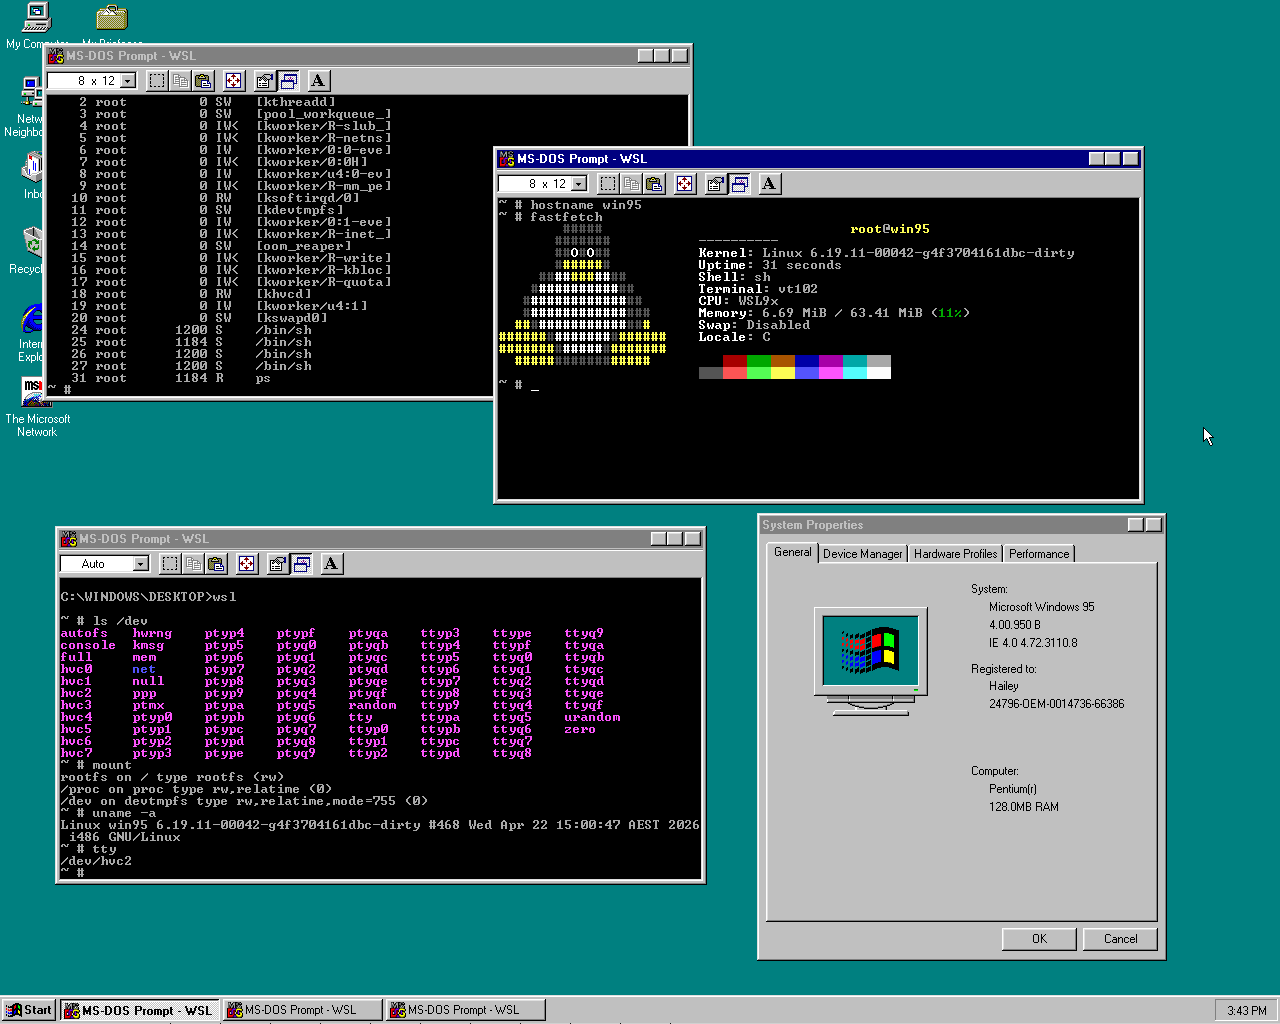
hailey@hails.orgWith Windows 9x Subsystem for Linux you can run all your favourite Windows and Linux apps side-by-side with a modern Linux kernel running cooperatively with the Windows kernel in ring 0. And unlike modern WSL, no hardware virtualisation is used so even your 486 can run it!
Please enjoy, I think this might be one of my greatest hacks of all time
https://codeberg.org/hails/wsl9x
 73
28
3
 repeated

feral mouse
algernon@come-from.mad-scientist.clubShow content
Today is Friday, and as every Friday, like clockwork, I will turn up the "mess with the crawlers" knob. Today is also the first of May, where we celebrate not one, but two birthdays: my Wife's and mine.
In good Hobbit tradition, on birthdays, we do not get presents. We give persents. On this beautiful day, here's my present to you all: some of the crawlers will happily honor Content-Disposition: attachment; filename="/lib/libc.so.6" and the like. Yes, they'll try to save the file to an absolute path of your choosing.
Now, they usually don't run as root, but there's so many other ways to exploit this vulnerability! Like, if a crawler was a bash script using curl without -q, ~/.curlrc would present a few fun opportunities.
Combine that with other exploits, such as copy.fail, and remember that many of the systems used for crawling are ancient and contain multitudes of such vulnerabilities.
Happy Friday!
0
1
0
Noisytoot
noisytootOpenWrt is still vulnerable to copyfail and doesn’t compile algif_aead as a module or include BPF-LSM support
Edit: it does, in fact, compile algif_aead as a module (kmod-crypto-user)
0
0
0
repeated
Yureka
yuka@fedi.yuka.devIf you are as annoyed as me about the fancy CVE-2026-31431 website not actually mentioning what Kernel versions to update to (only mentioning the commit rev), I translated this for you by looking through the releases manually and checking if they contain the fix.
The following upstream kernel tags contain the fix:
6.6.137+
6.12.85+
6.18.22+
6.19.12+
7.0+
But of course your distro might also apply the patches on any other version, and they will hopefully provide that information.
Edit: added 6.6/6.12 versions
13
7
0